Security · Security by default

Secure by default. Documented for your auditors.

Confidentiality, integrity and availability are covered by our documented technical and organisational measures (TOMs). We are certified to ISO/IEC 27001 and ISO 9001. Where needed, we add targeted extras.

ISO/IEC 27001 and ISO 9001 Uptime Institute Tier IV data centres Encrypted backups Brute-force protection
Jump to
Use cases

Sound familiar?

“We have to prove who has access to what.”

How we help

Access is managed through authorisation concepts with a minimum number of administrators. Access to applications is logged, as documented in our TOMs.

“We want to know who is responsible for what.”

How we help

On a Managed Server, we install security patches for the software we provide on an ongoing basis. Updates of your own software stay with you. On a Root Server, you manage the system and your backups yourself.

“We need extra protection.”

How we help

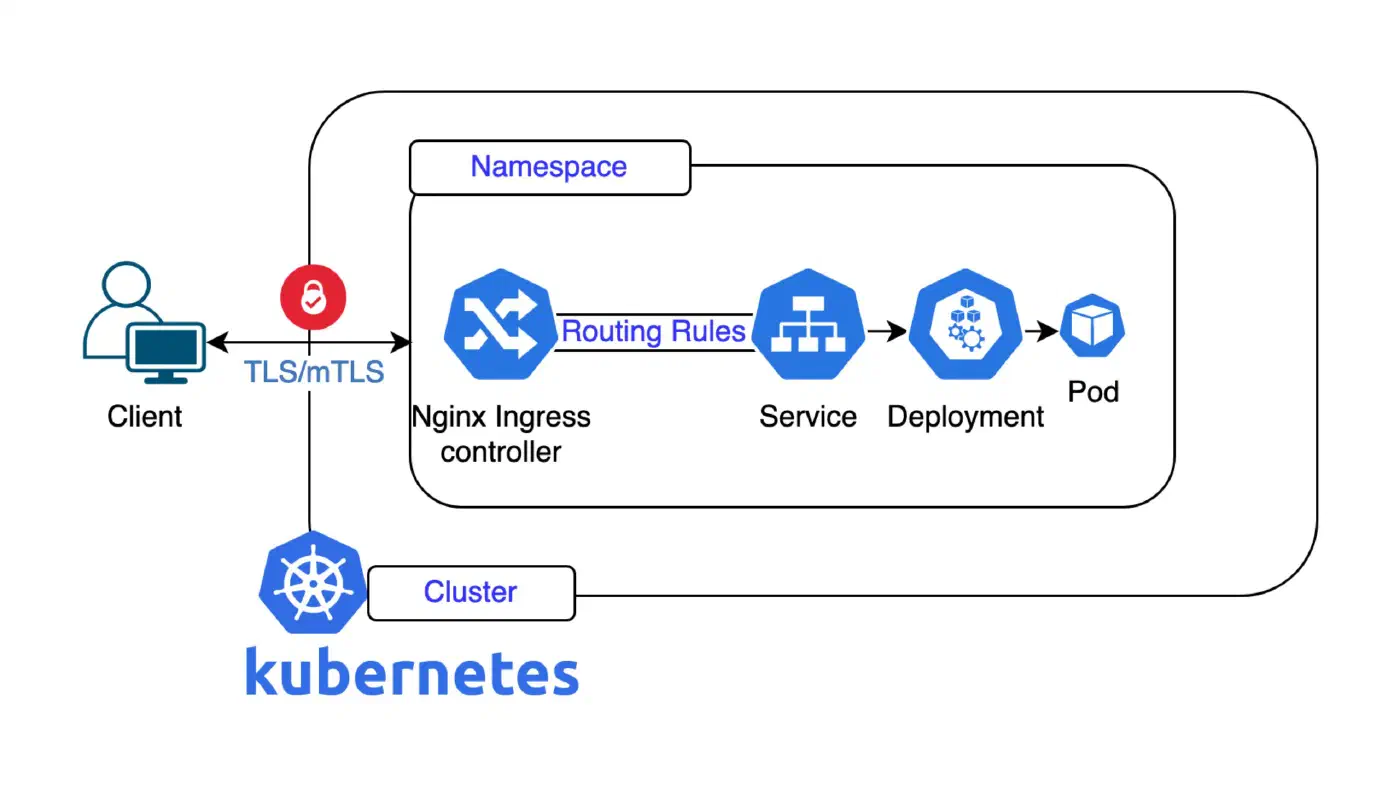
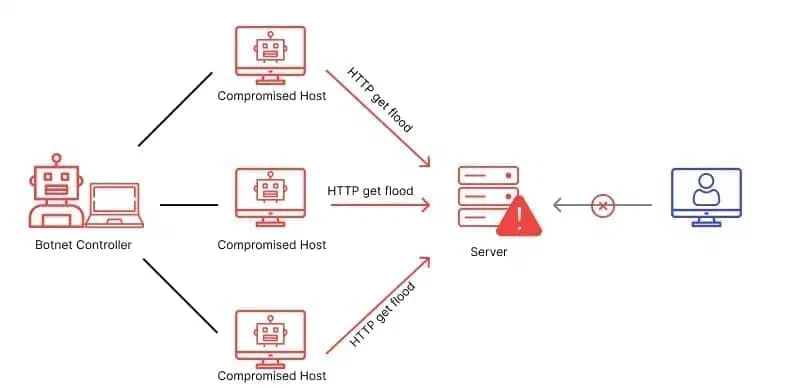
DDoS protection and a web application firewall with Cloudflare, mod_security on your Managed Server (installed, deactivated by default) or Airlock Microgateway WAF in your Managed Kubernetes cluster.

Our principles

How we ensure security

Certified

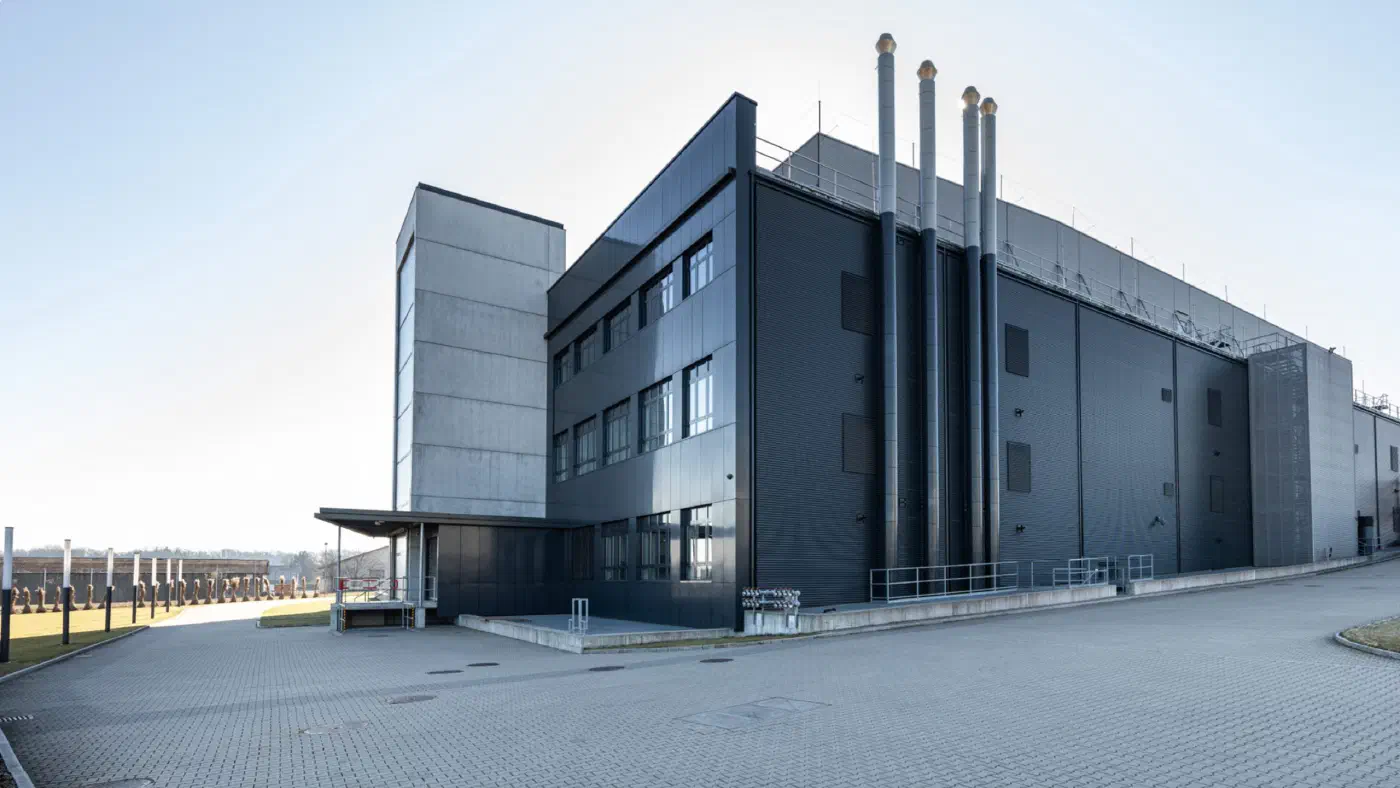
We are certified to ISO 9001 and ISO/IEC 27001. Both data centres, NTS / ColoZüri and NTT Zürich, are Uptime Institute Tier IV.

Physical security

Personnel and goods lock with biometric access control at NTS / ColoZüri, badge access after identity verification by security guards at NTT Zürich. Video surveillance of the entrances and gas fire extinguishing.

Brute-force protection

On Managed Servers, an IP address is blocked for 60 minutes after the tenth failed login for SSH, SFTP, FTPS and FTP, and for one week after repeated attempts.

Patching

Managed Servers run Ubuntu LTS, for which Canonical backports security patches. We install them on an ongoing basis and in the weekly maintenance window. We also explain how to read security scan reports for your server.

Encrypted backups

Managed Server backups are daily, encrypted and stored in two separate data centres for 7 days.

Incident handling

Documented processes for detecting, reporting and handling security incidents, involving our information security officer and our data protection officer.

Trust

What customers say

«The implementation of the new hosting solution proceeded perfectly; Nine was a cooperative, proactive partner.»
Roland LooserVerantwortlicher Web/Print

Questions about security or compliance?

We’ll show you how we cover your requirements.

Talk to our experts

Do you have questions about our products? No problem. Contact our sales department or go directly to your Cockpit to see all the possibilities at Nine.

Subscribe to our newsletter for the latest updates: