 Status


Same Ingress, Different Defaults: What Changed When We Moved to HAProxy
We moved our managed services and Deploio from ingress-nginx to HAProxy. Eight defaults behaved differently. Here is …
Built on open standards with no vendor lock-in, NKE is CI/CD & DevOps-ready out of the box, so your …
Our Managed Servers run on fast NVMe SSD storage and support PHP, Node.js, Python, Ruby, MySQL, …
Deploio is our fully managed Swiss app engine and PaaS that automatically builds and deploys on …
Using our Root Dedicated Servers, you benefit from our powerful infrastructure on two independent …
Choose from multiple NVIDIA GPU models with thousands of CUDA cores and dedicated Tensor Cores, …
MySQL, MariaDB, PostgreSQL or Redis-compatible Key Value Store – as a fully managed DBaaS hosted in …
Our SLAs give you binding incident response times, service credits if we don't deliver, and access …
Your data stays in Switzerland with full data residency guarantees, free from the CLOUD Act and …
House your hardware in our Zurich facilities with 99.9% uptime SLA, backed by 2N redundant power at …
Our managed in-memory data stores accelerate your read-heavy workloads by keeping frequently …
Our Managed Shibboleth gives you enterprise-grade authentication with fine-grained attribute release …
Our Managed Solr runs on SolrCloud architecture for distributed, highly available search across your …
Our Managed OpenSearch gives you a production-ready search and analytics platform with built-in …
Our vClusters give each team their own API server and dedicated control plane with RBAC (role-based …
Our Cloudflare integration protects your applications with machine learning-powered threat detection …
Airlock Microgateway is a Kubernetes-native web application firewall (WAF) from Swiss manufacturer …
Security is an integral part of how we design and operate secure cloud infrastructure and services. …
We moved our managed services and Deploio from ingress-nginx to HAProxy. Eight defaults behaved …
At TechTalk #29, Thomas Jaggi (LegacyNotes) showed live how much modern browsers and Node.js now …
In August 2026, a large DDoS attack hit a customer and our own network directly. What happened, …
At TechTalk #29, Lena Fuhrimann (bespinian) shared a practical guide to running fast, private LLMs …
At TechTalk #29, Sebastian Nickel walked us through our journey from Ingress-NGINX to HAProxy and …
An overview of how to manage your infrastructure at Nine through code: the Nine API, nctl, Deploio, …
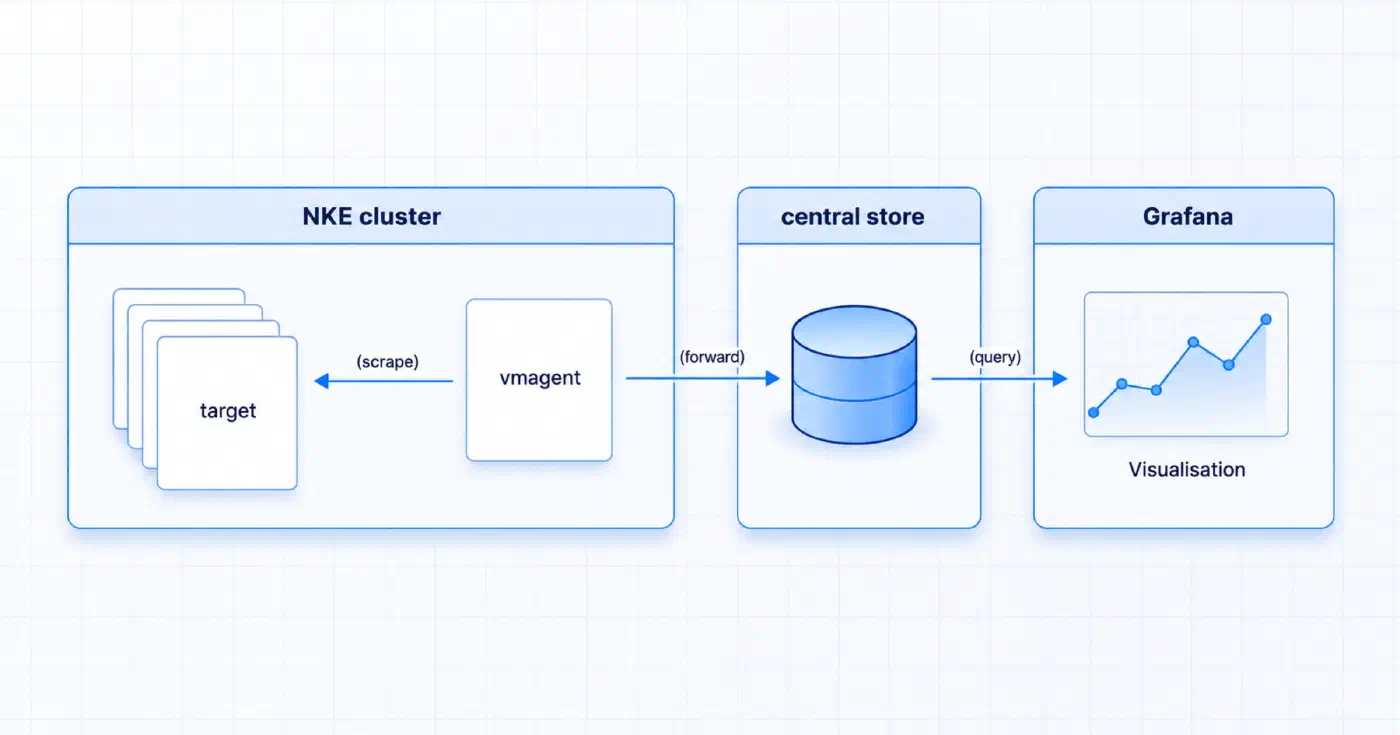
We are excited to announce the release of the NKE Metrics Agent, a new way to handle application …
Ubuntu Resolute brings mostly evolutionary updates for our Managed Servers, a recent kernel and one …
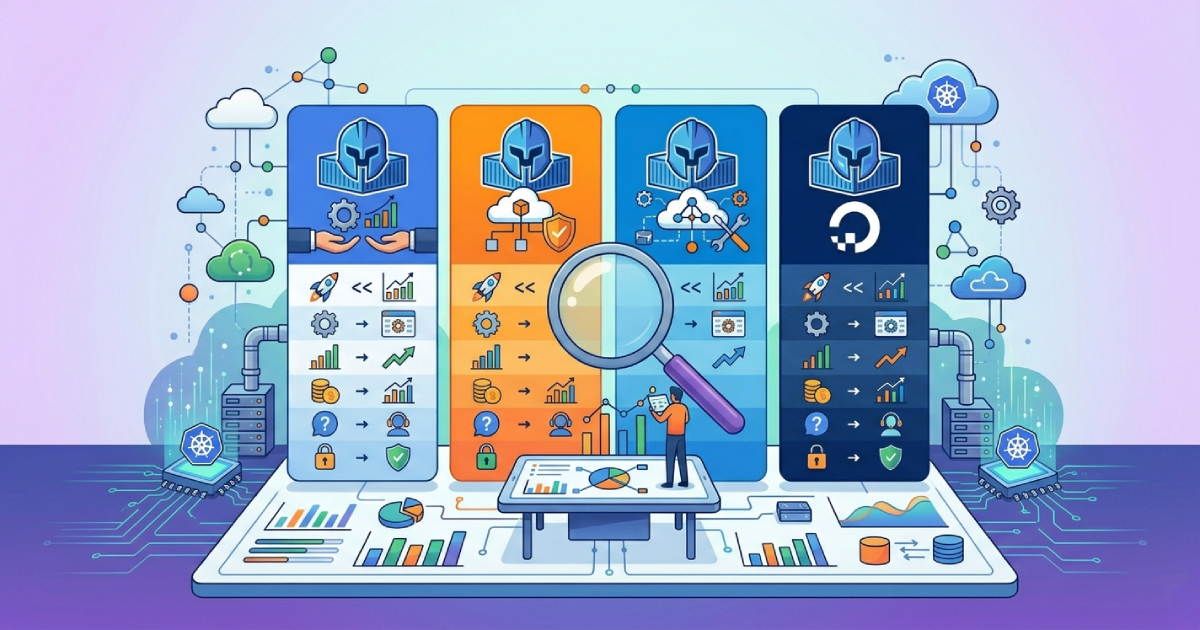
Self-hosted, Exoscale SKS, hyperscaler, VSHN, Swisscom, Infomaniak, or NKE: an honest comparison of …
Cluster upgrades three times a year, observability, secret management, network policies: Kubernetes …
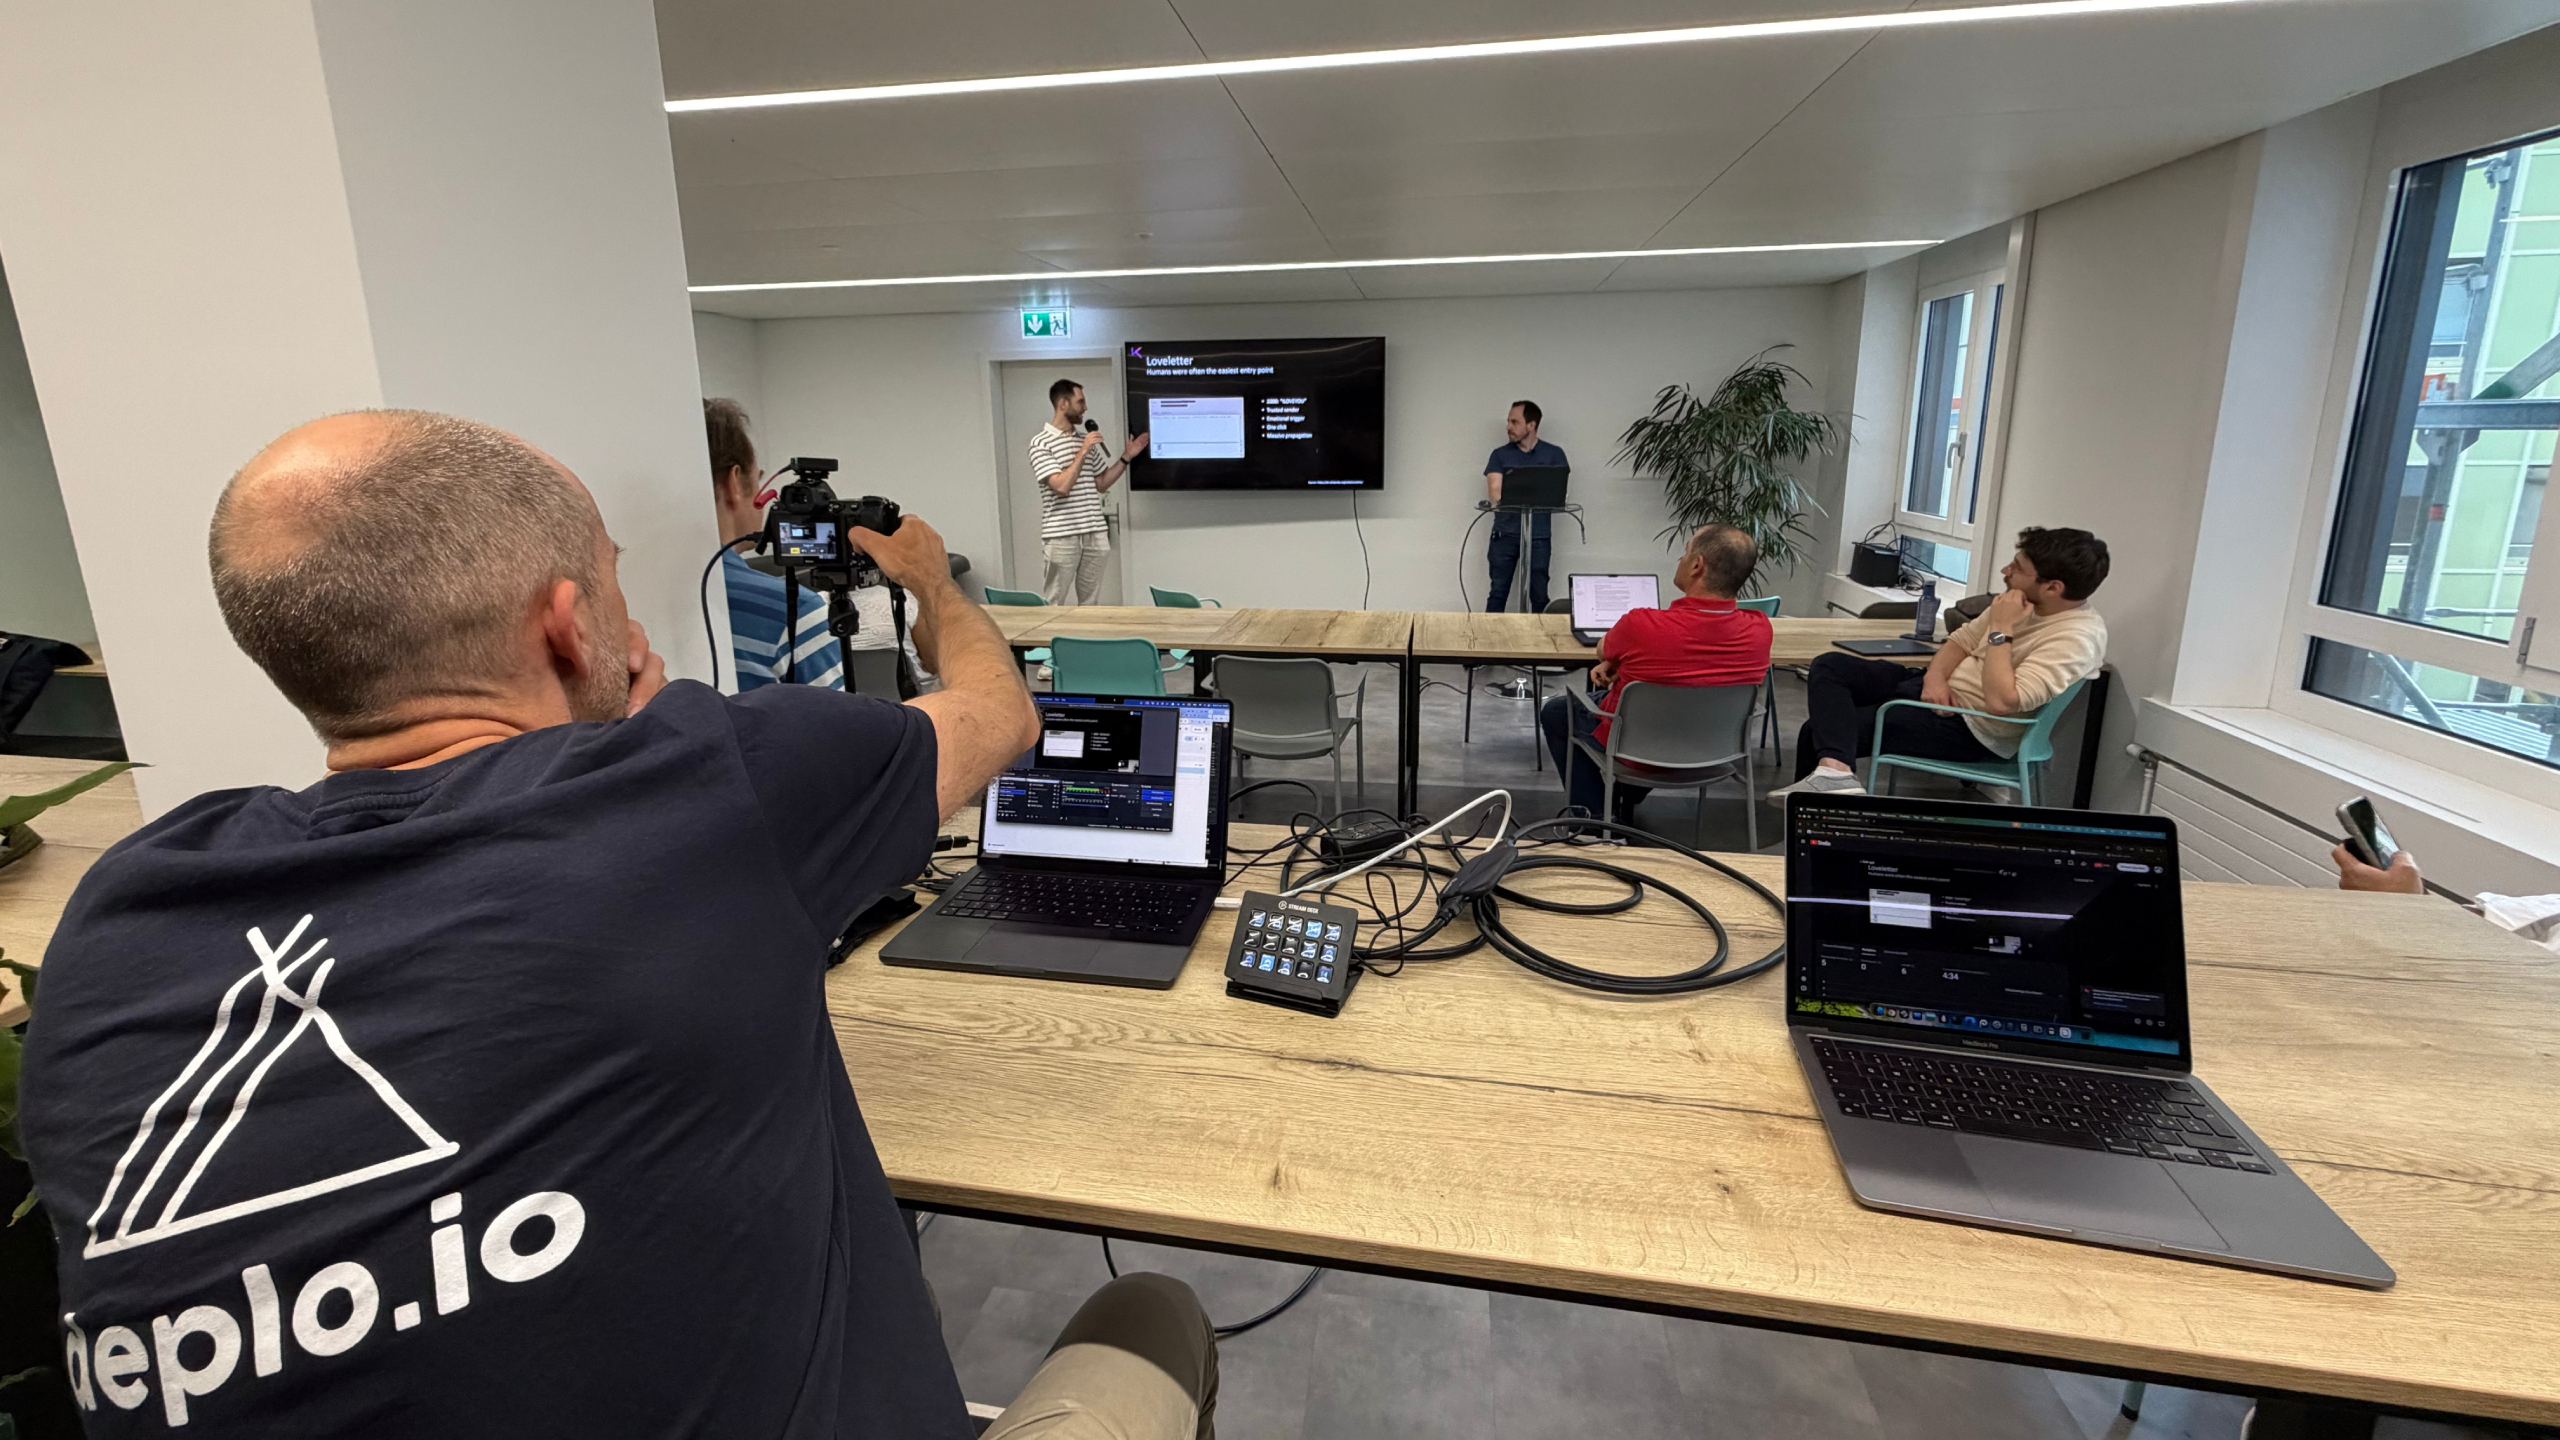
At TechTalk #28 we explored non-human identities as an attack surface, navigating complexity in …
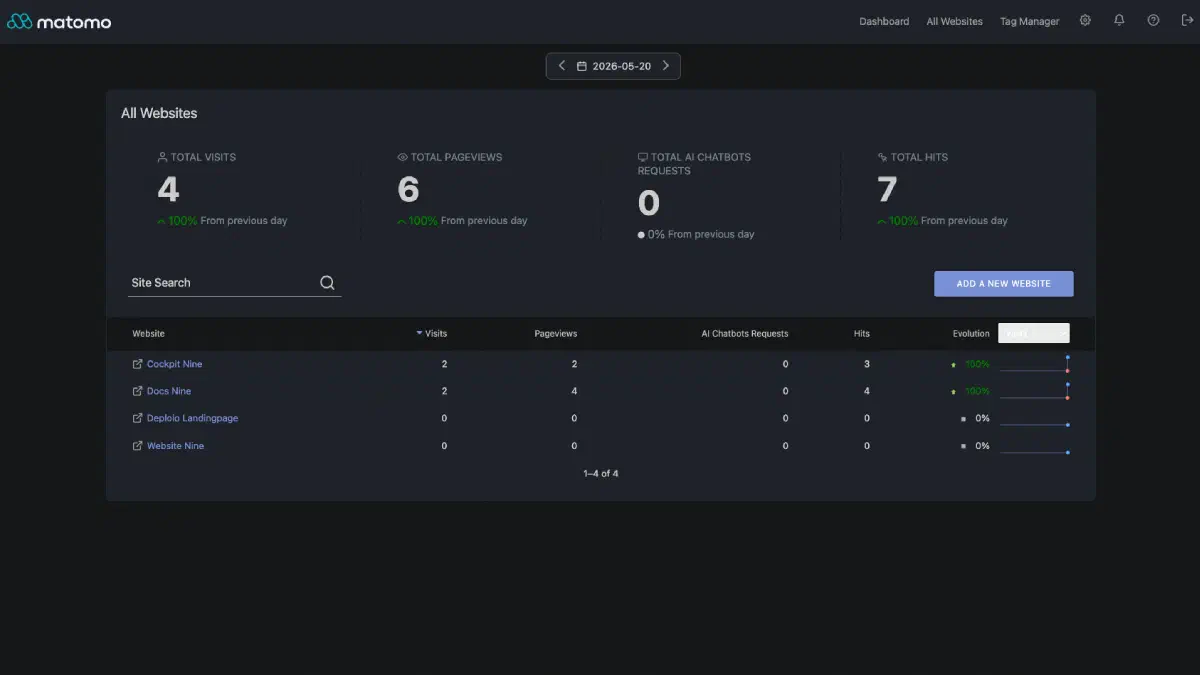
We replaced Google Analytics with a self-hosted Matomo instance running on our own infrastructure in …
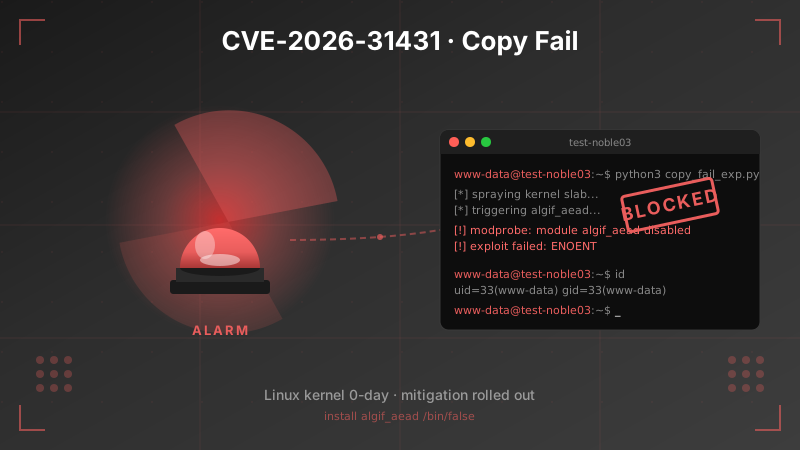
On April 30, 2026, a 0-day in the Linux kernel was disclosed: root with a few lines of Python, and …
CLOUD Act, data sovereignty and AI compliance: why Swiss companies shouldn't run their LLM workloads …

Our first TechTalkThursday of 2026 – number 27 in our event series – took place on the 10th of March …
One Slack message, a seamless migration – and finally cloud hosting from Switzerland. How Renuo …
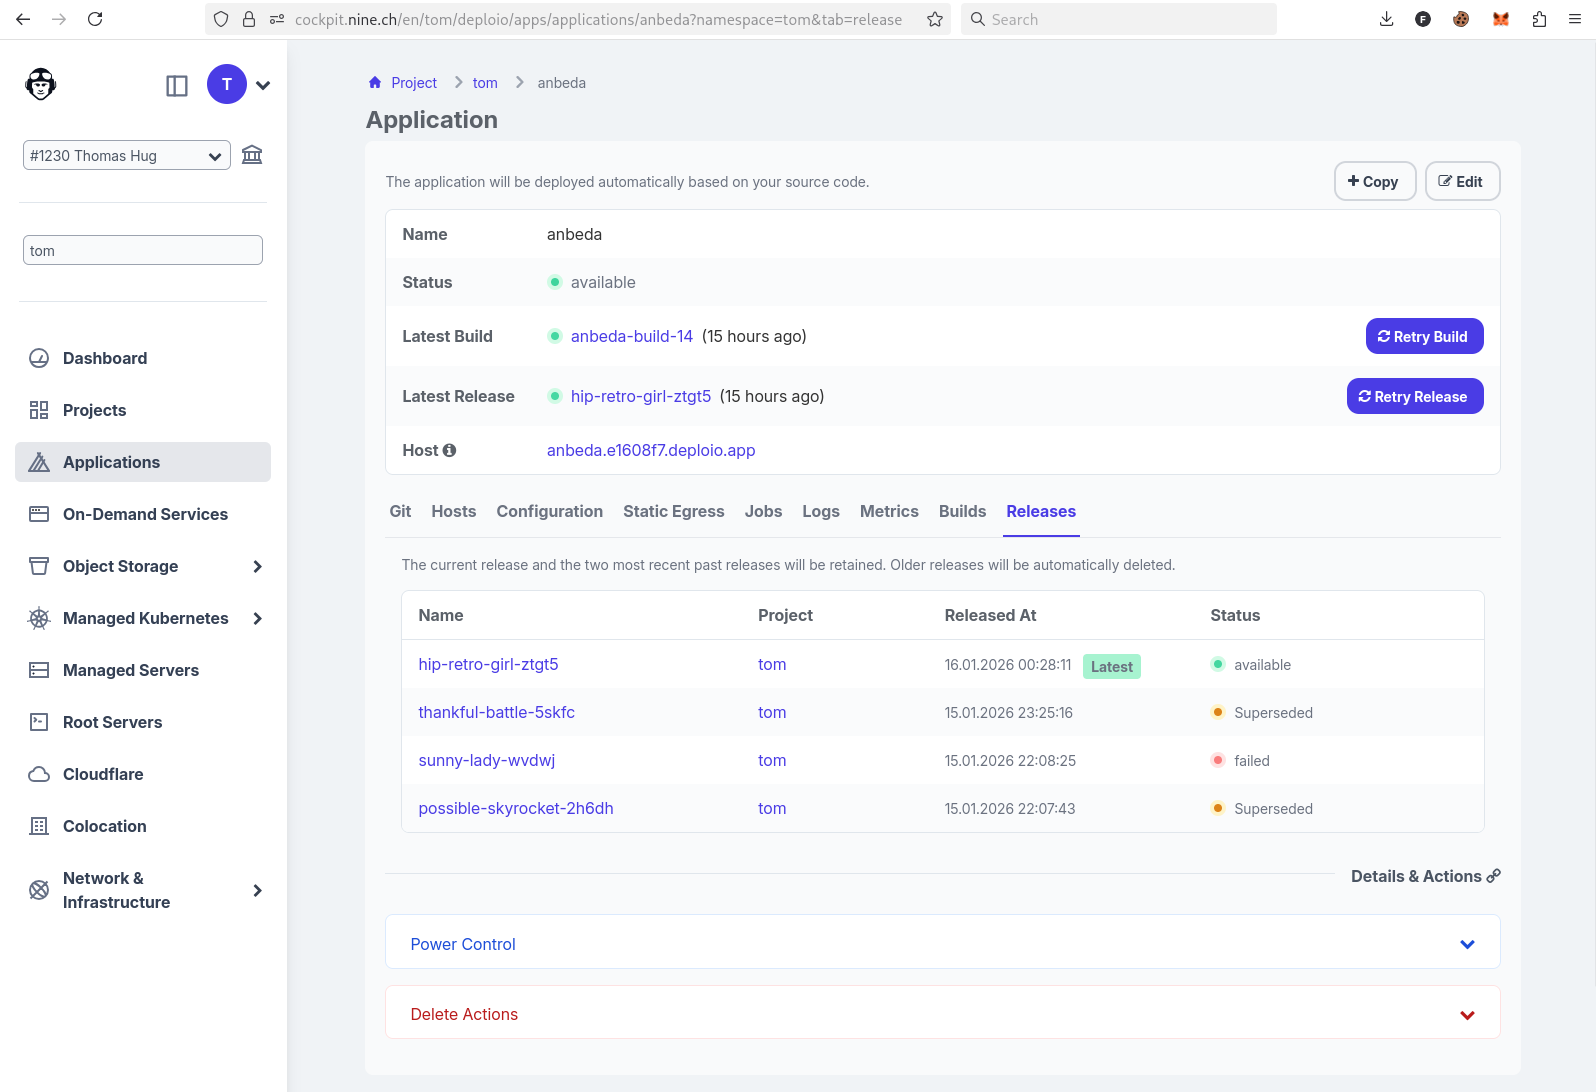
An old Angular 4 app that's been running on a server since 2017 – one that should have been updated …
We migrated our website from WordPress to Hugo. In this article, we explain why we made this move …
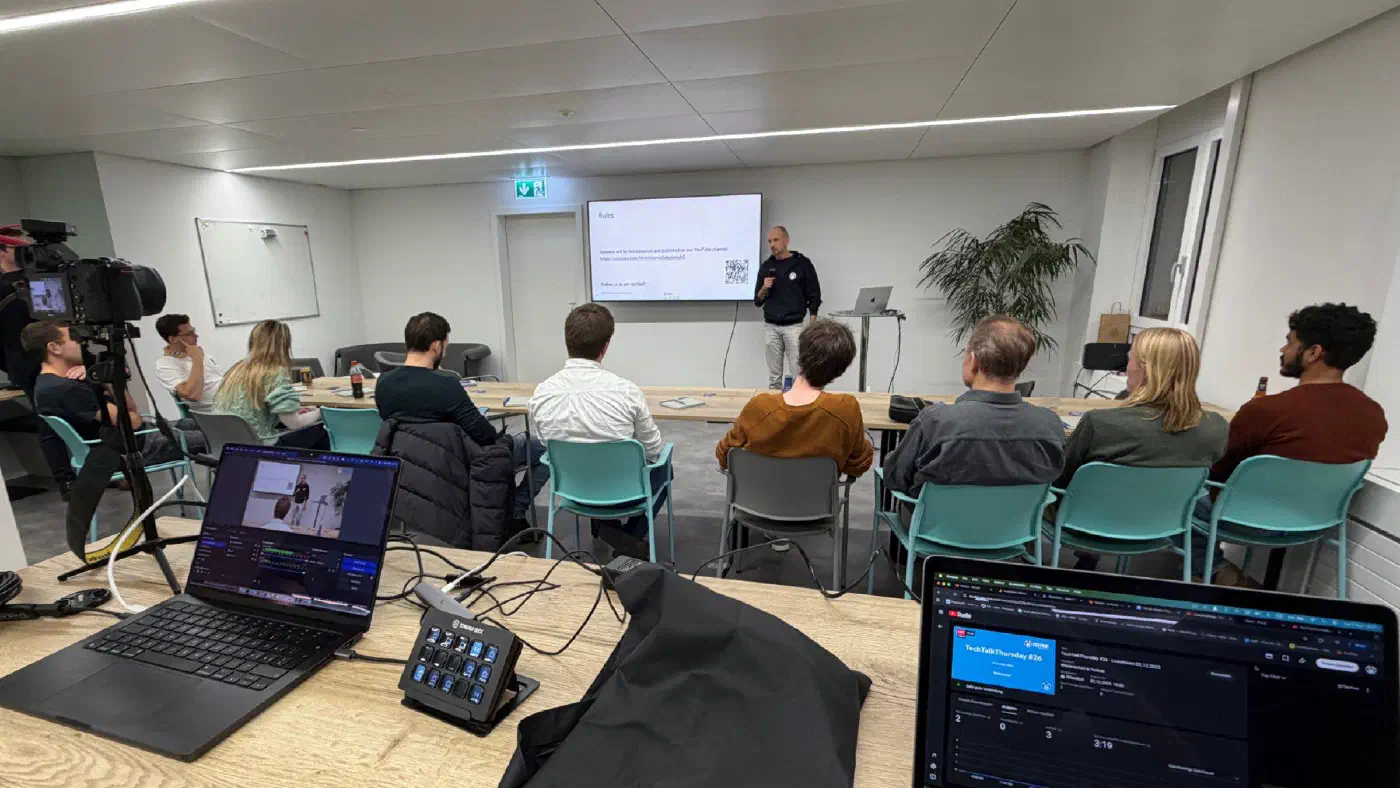
Our fourth and last TechTalkThursday in 2025 – it was number 26 of our event series – took place on …
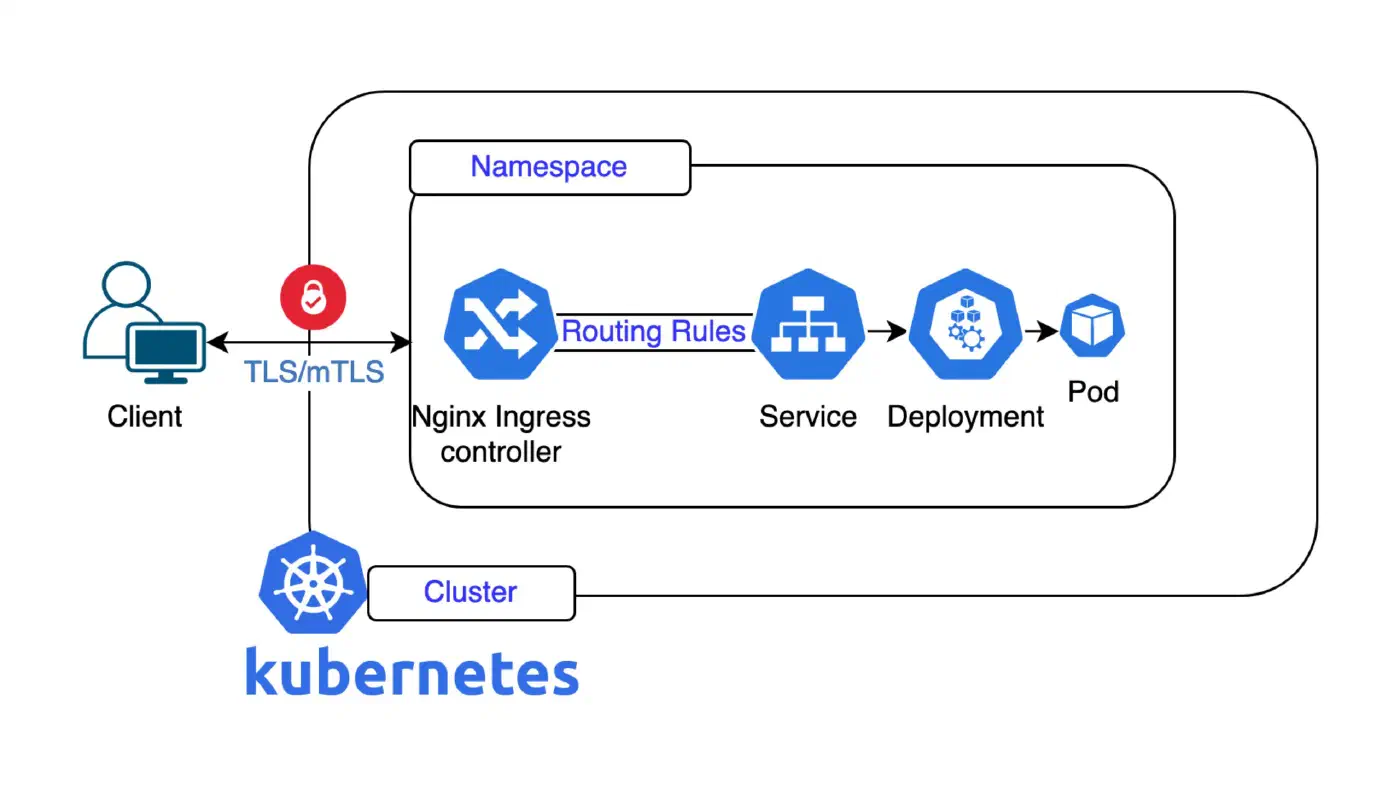
We're currently working on a proper strategy relating to the upcoming retirement of the …
In the digital world, server security is not a “nice-to-have” but one of the cornerstones of a …
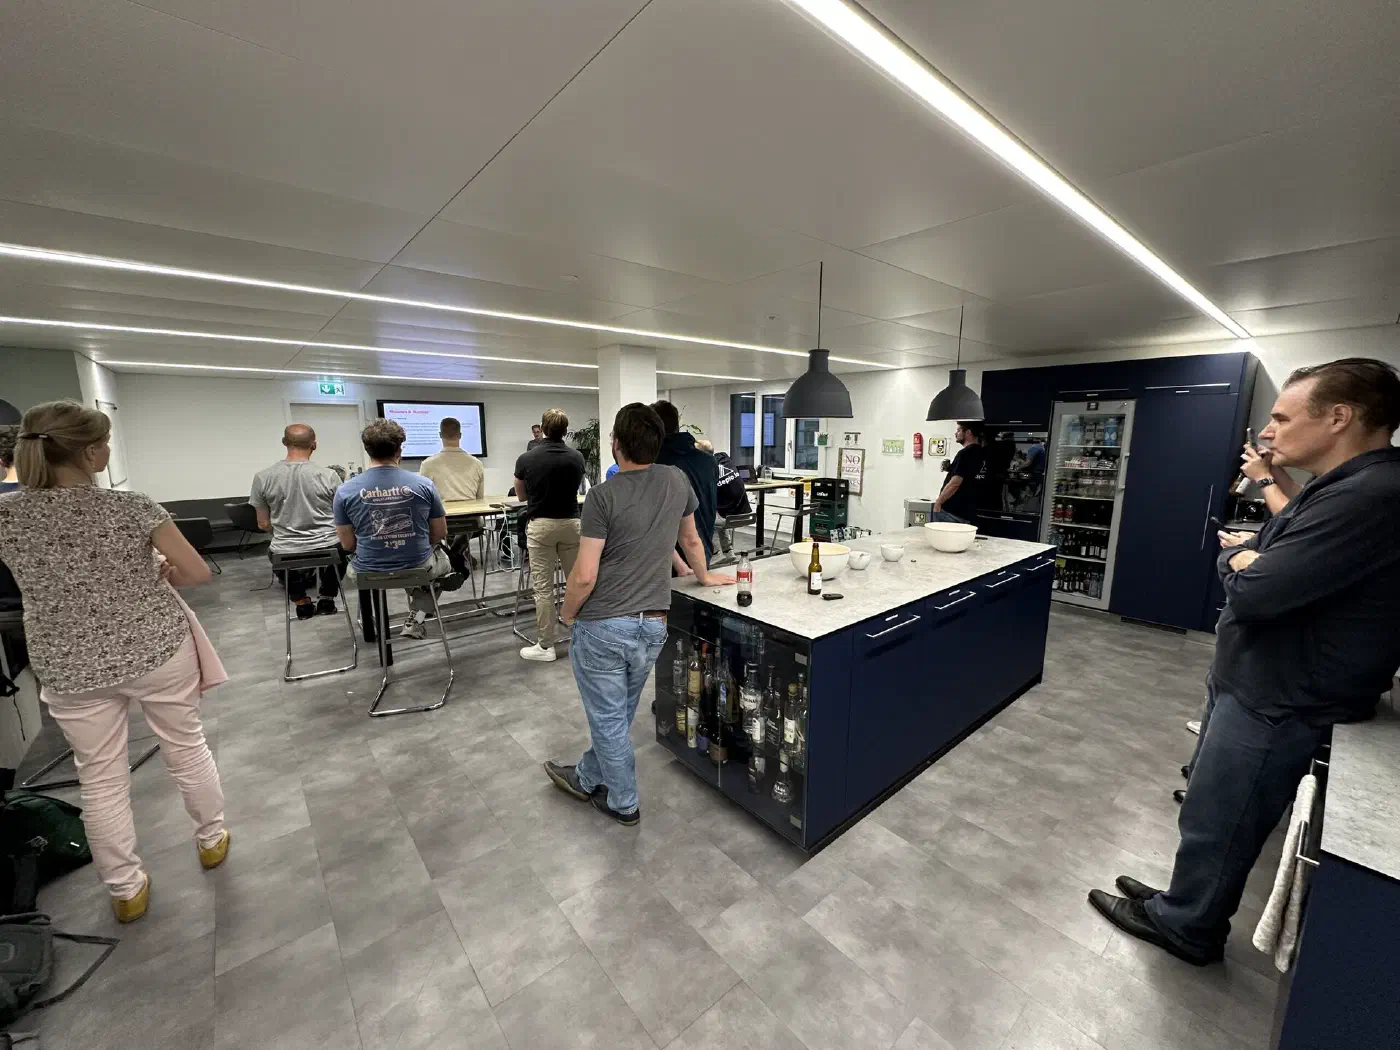
Our third TechTalkThursday in 2025 – it was number 25 of our event series – took place on the 4th of …
«Digitalisation is the path to a sustainable future.» This statement applies in many areas – but it …
Our second TechTalkThursday this year was number 24 of the event series and took place on the 5th of …
Data protection is no longer just a «nice to have». For many organisations, it has become an …
One common pattern we've observed at Nine is that many of our customers run web applications — think …
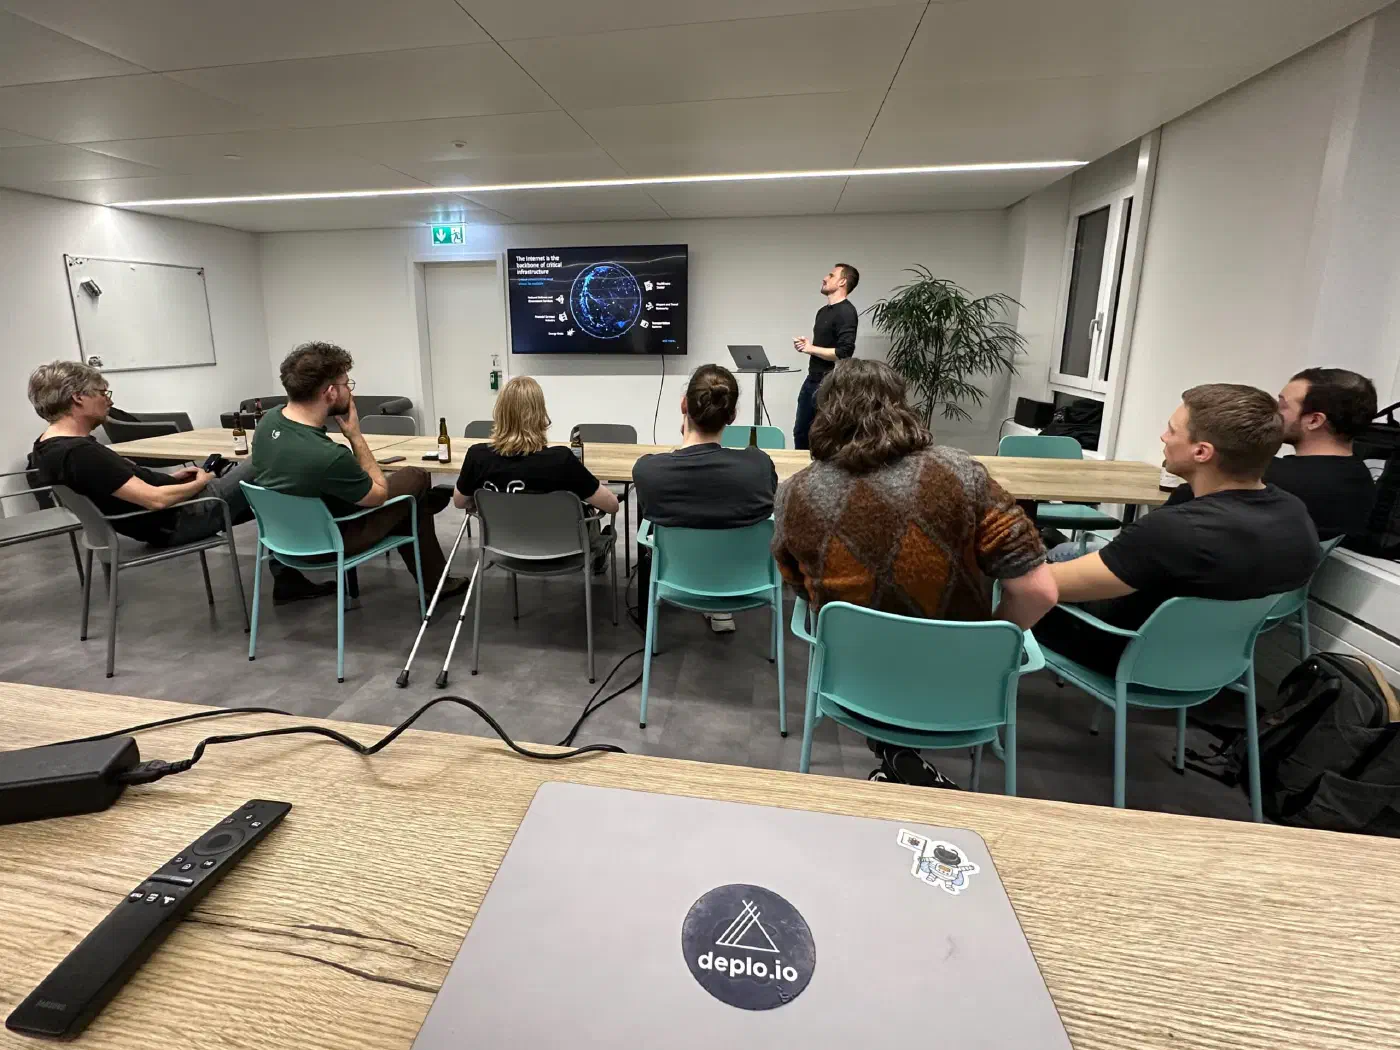
The first TechTalkThursday in 2025 – and number 23 of the event series – took place on the 6th of …
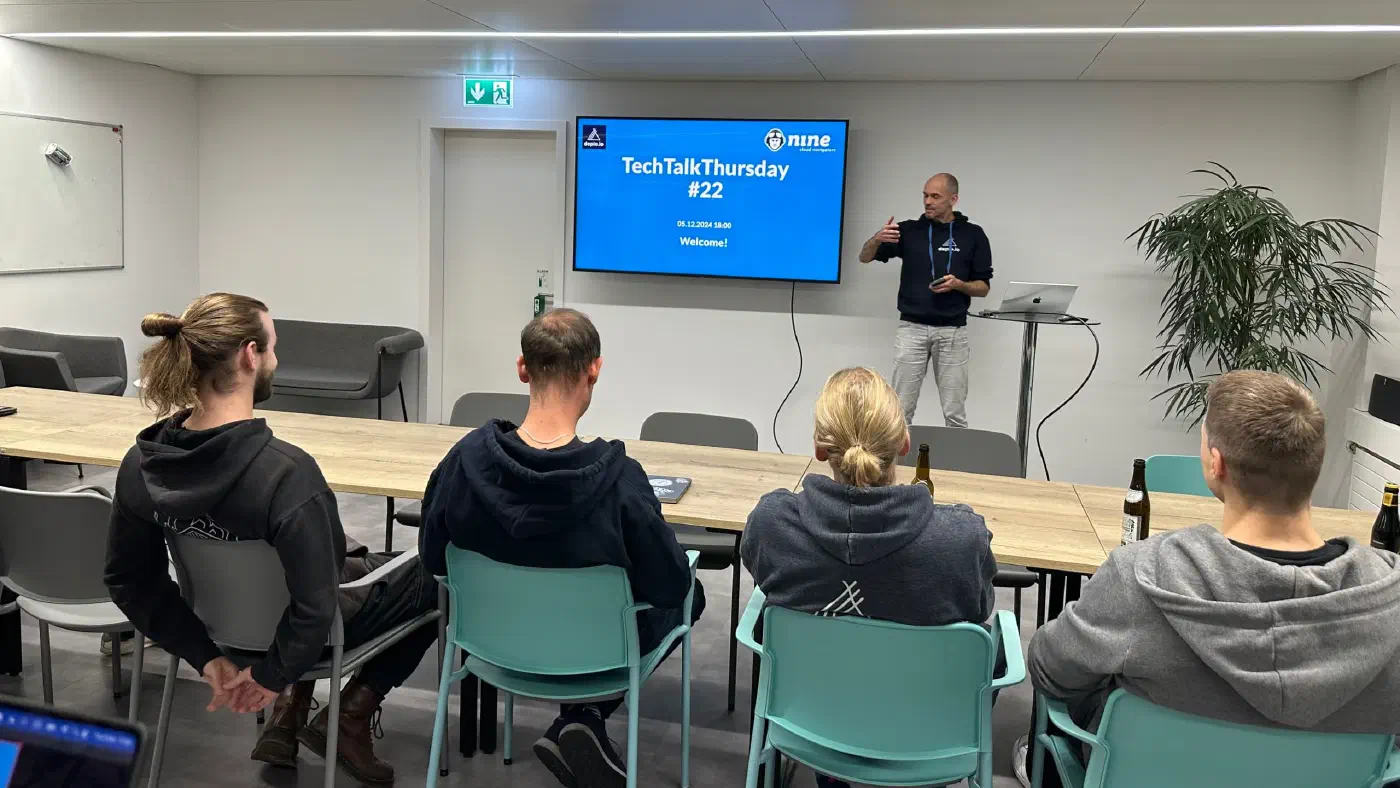
Our TechTalkThursday #22 took place on the 5th of Dezember 2024 at 18:00 in our office. We were …
With the first snow, we were enticed by the mountains: Our coworking retreat took place at the base …
Web development has evolved significantly, with numerous tools and frameworks streamlining the …
Every company wants its products and services to be seen. This requires a marketing professional who …
In today’s rapidly evolving tech landscape, modern systems like Kubernetes are often seen as the …
At Nine, we’ve been hard at work refining Deploio, our platform for deploying applications with …
Every company needs someone with a flair for numbers. An expert who has debtors and creditors under …
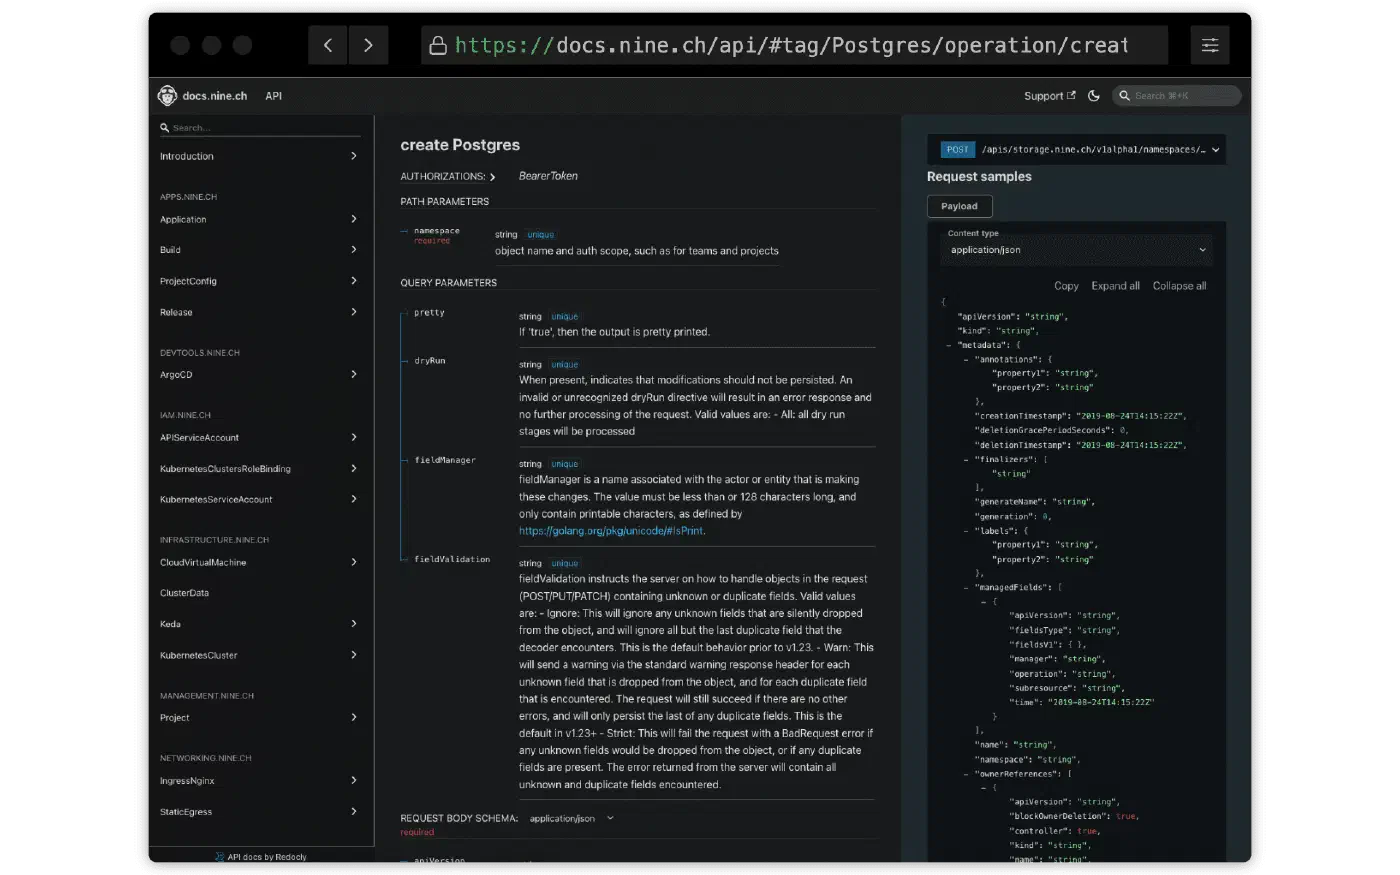
Our on-demand MySQL and PostgreSQL databases are now available for your production workloads. Let's …
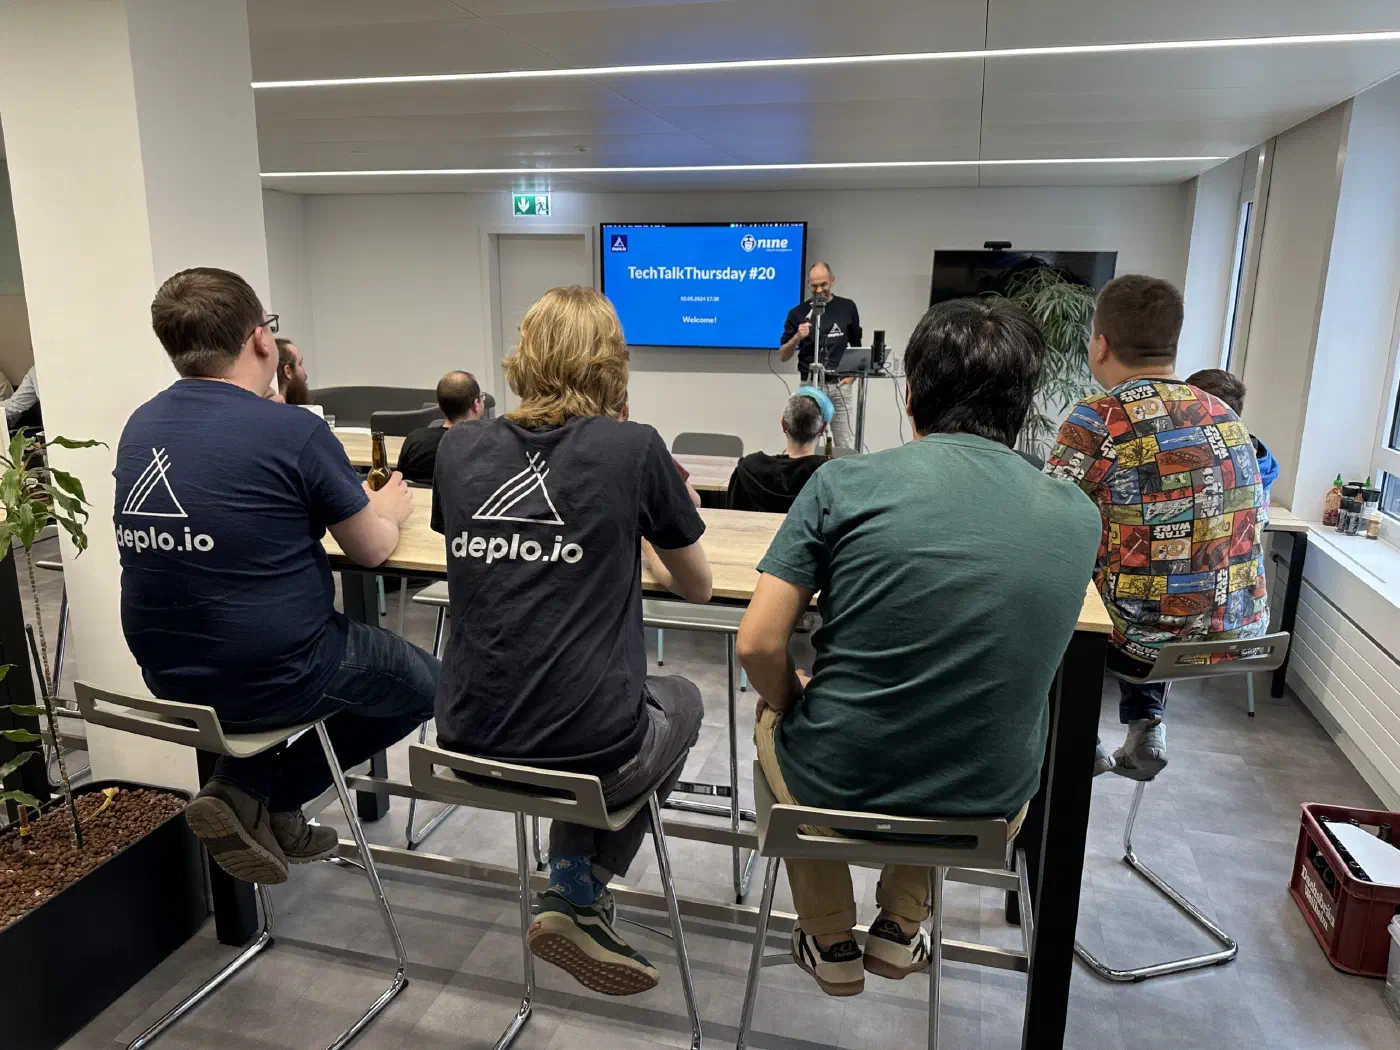
Our TechTalkThursday #20 took place on the 2nd of May 2024 at 18:00. We were happy to welcome two …
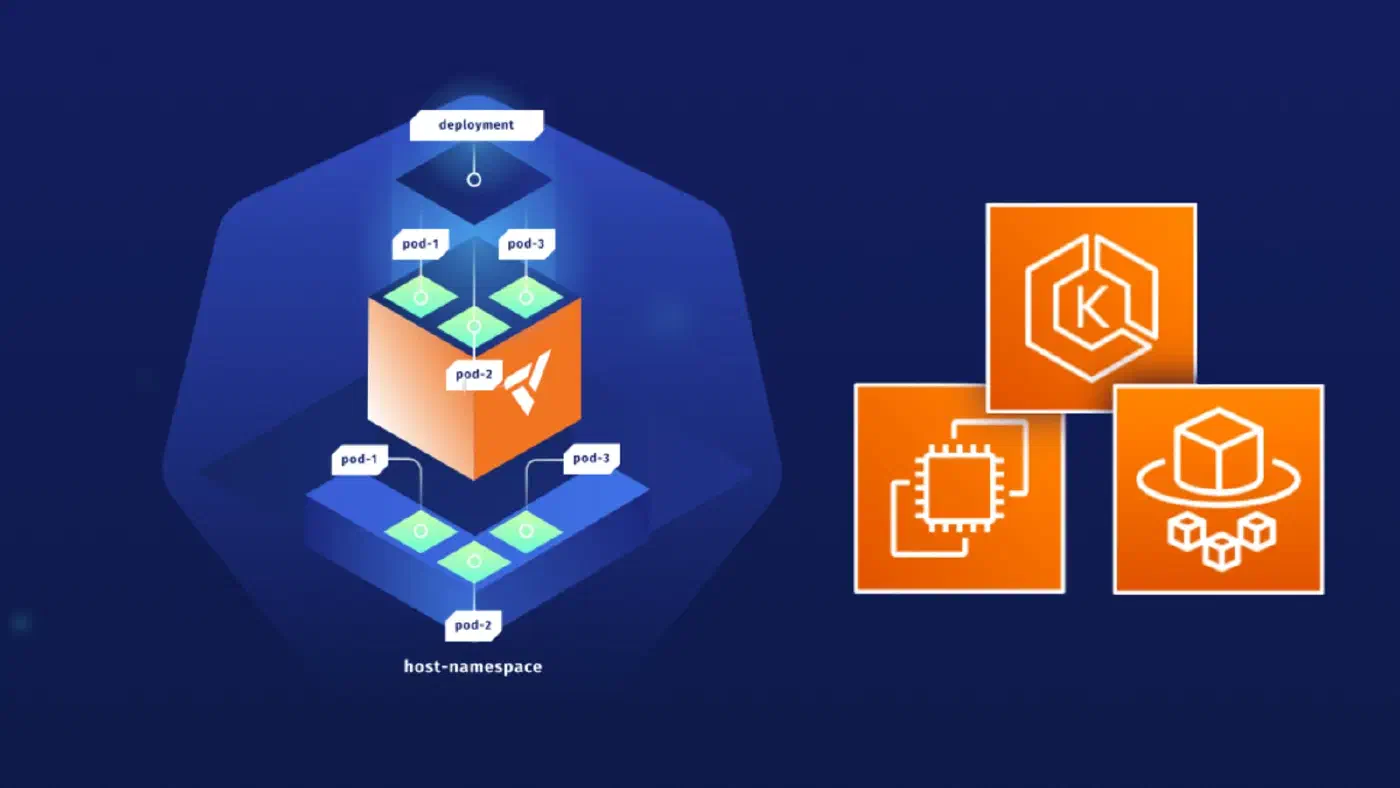
A virtual cluster is a fully working Kubernetes cluster that runs on top of another Kubernetes …
In today's web applications, search functions are omnipresent. Searching for product titles or …
As you may have noticed, our v1 S3 product has officially been deprecated, and the migration to v2 …
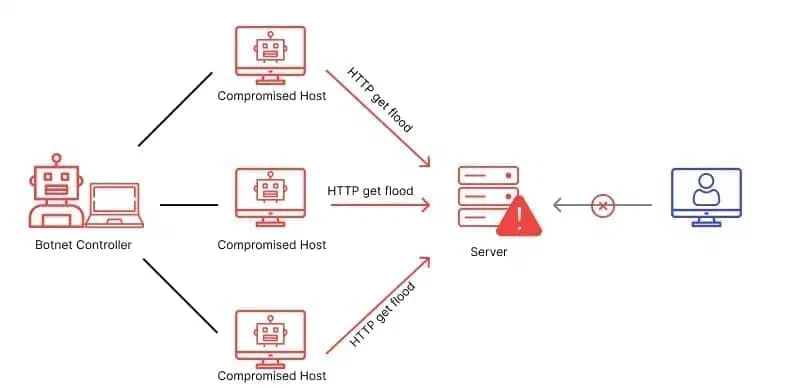
What is HTTP? HTTP, the Hypertext Transfer Protocol, is the 'language' that your web browser and …
No company can run efficiently without customer support. This is no different at Nine: every day, we …
When talking to people about migrating their applications to Kubernetes, there are often questions …
Today we’re lifting the curtains and are thrilled to present: Deploio, our Swiss-made, next-gen app …
Our previous support page had lost its luster over the years. Originally developed in-house using …
The new federal Act on Data Protection (nFADP) will take effect in Switzerland from 1 September …
As more developers get familiar with deploying to Kubernetes, the need for better isolation between …
Modernise your web services with our new API and CLI tools. At Nine, we're always looking for …
As we launch our API we want to give some technical insights on how we got here and what can be …
Elasticsearch/OpenSearch and Solr are among the most popular and powerful open source search …
Three growth challenges digital agencies face as they scale, and how to overcome them Digital …
Having the reliability and mature APIs of global-scale cloud providers offers the possibility of a …
Self-service has become ubiquitous beyond the IT sector. Nevertheless, self-service cannot solve …
apfelkiste.ch is one of Switzerland’s biggest online shops. In 2020, it saw a turnover of 60 m Swiss …
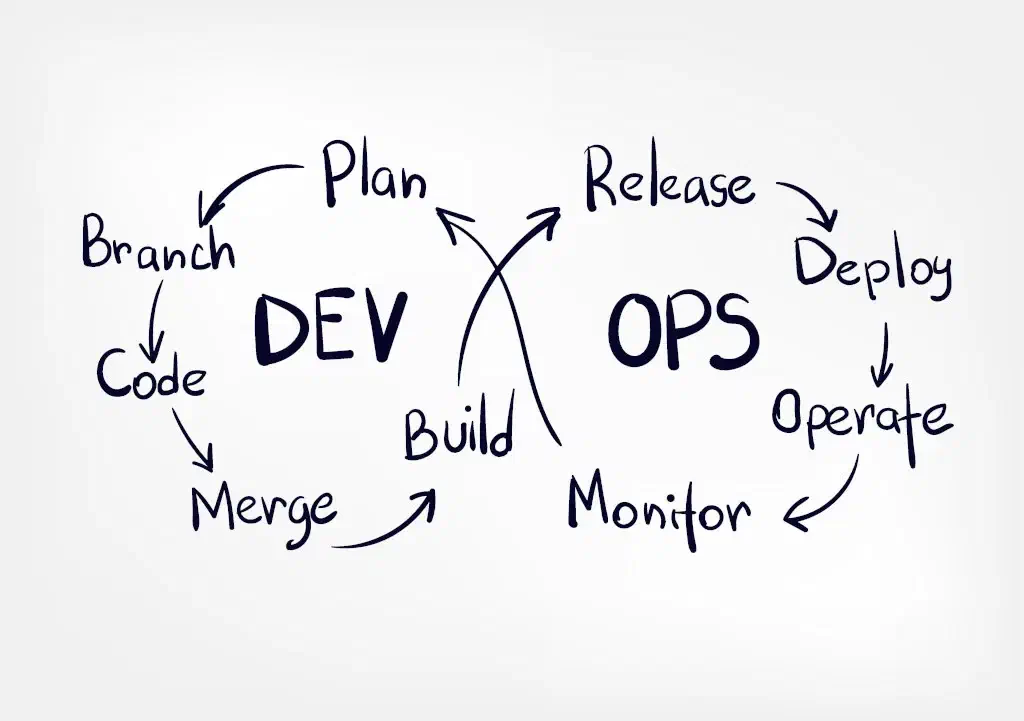
When development and operations are in tension, separate teams, each with their own self-image and …
The biggest cloud migration challenges in 2021 One thing that we often hear at Nine, being a Managed …
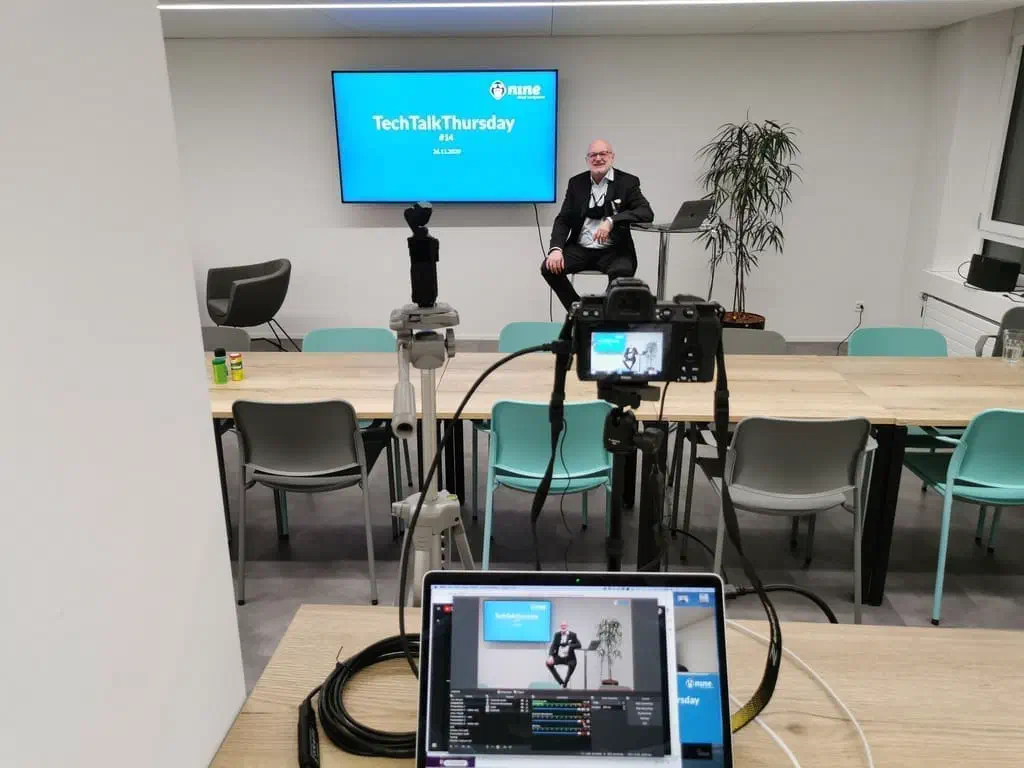
Our TechTalkThursday #14 took place on the 26th of November 2020 at 18:00. Due to local …
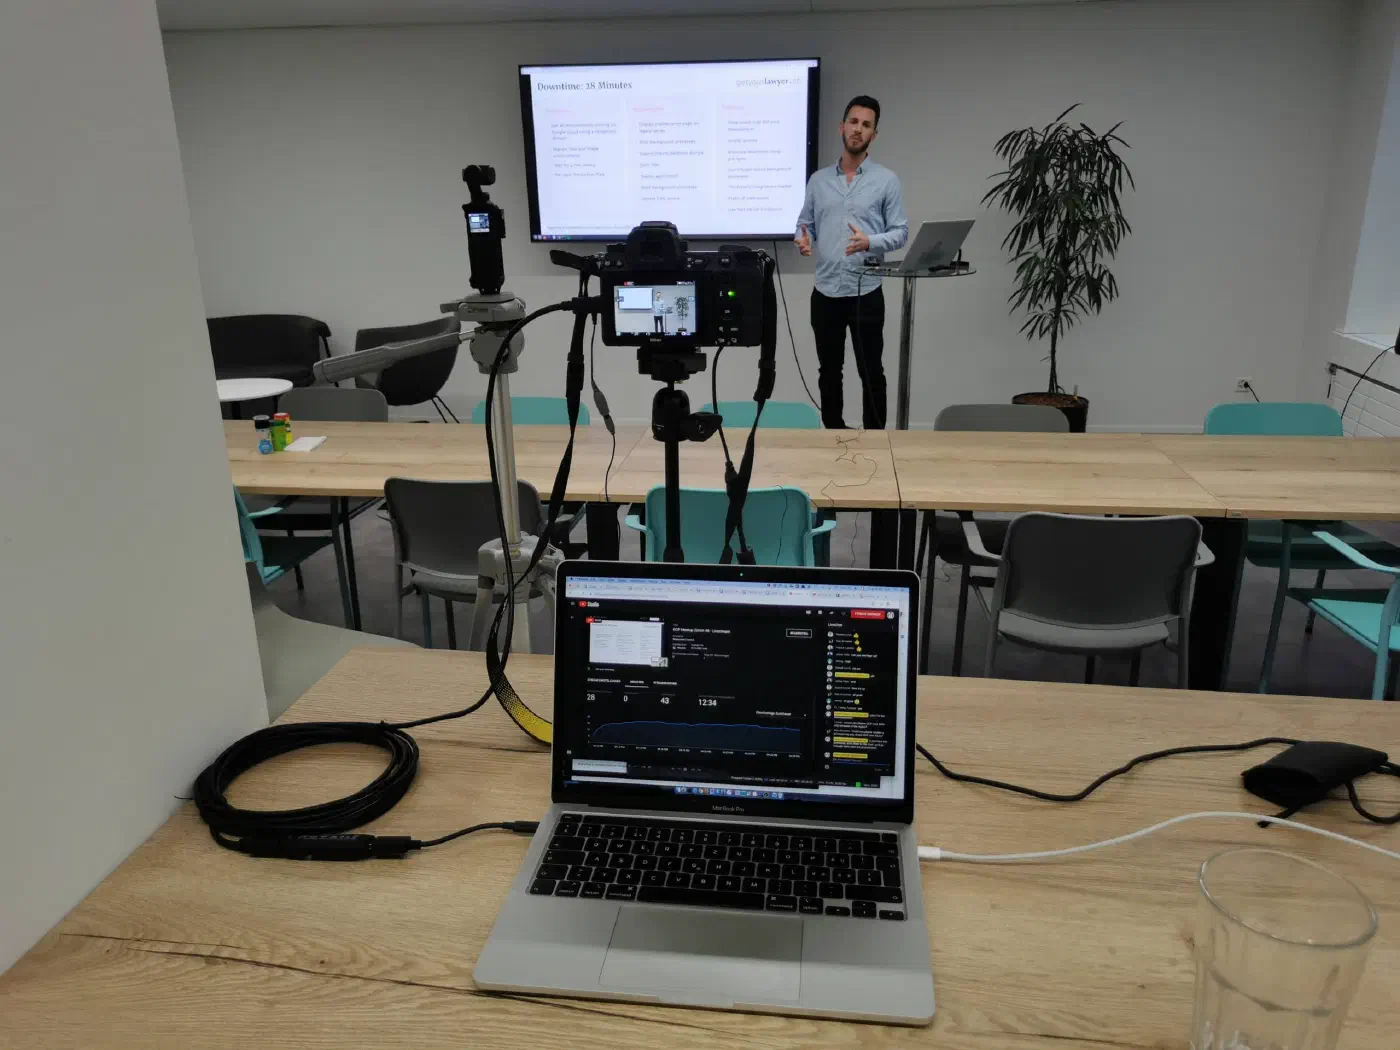
The Google Cloud Meetup #6 took place on November 10, 2020 in Zürich City in the cafeteria of Nine. …
Announcing: The newest Ubuntu distribution-release is now available for our “Managed Servers”. New …
Our TechTalkThursday took place on the 1st of October at 18:00. We had with only 15 participants …
Besides our normal TechTalkThursdays in the evening, we tried new times during lunch and at 08:00 in …
Benjamin Kuster, Sales Development Executive at Nine who reduced his work quota to 20% to found a …
Managed Service Providers are indispensable service providers and partners for a large number of …
The Google Cloud Meetup #5 took place on 25 August 2020 in Zürich City in the cafeteria of Nine. …
Virtualization, containers and cloud computing have fundamentally changed the development and …
Cloud computing has been established for a long time. The advantages over the classic supply of IT …
We quite often receive requests like: Do you support Docker? These requests kept growing, and …
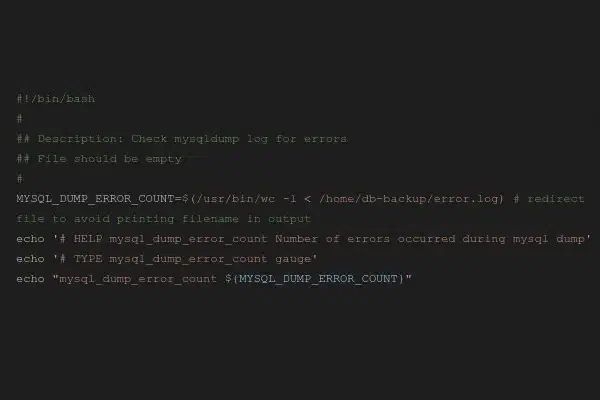
After having previously introduced our new monitoring system Prometheus in this blog, which replaced …
Clouds are servers, or networks of servers, on which corporate applications or services are provided …
Our TechTalkThursday took place on the 4th of June at 18:00. As Corona is not yet over and since we …
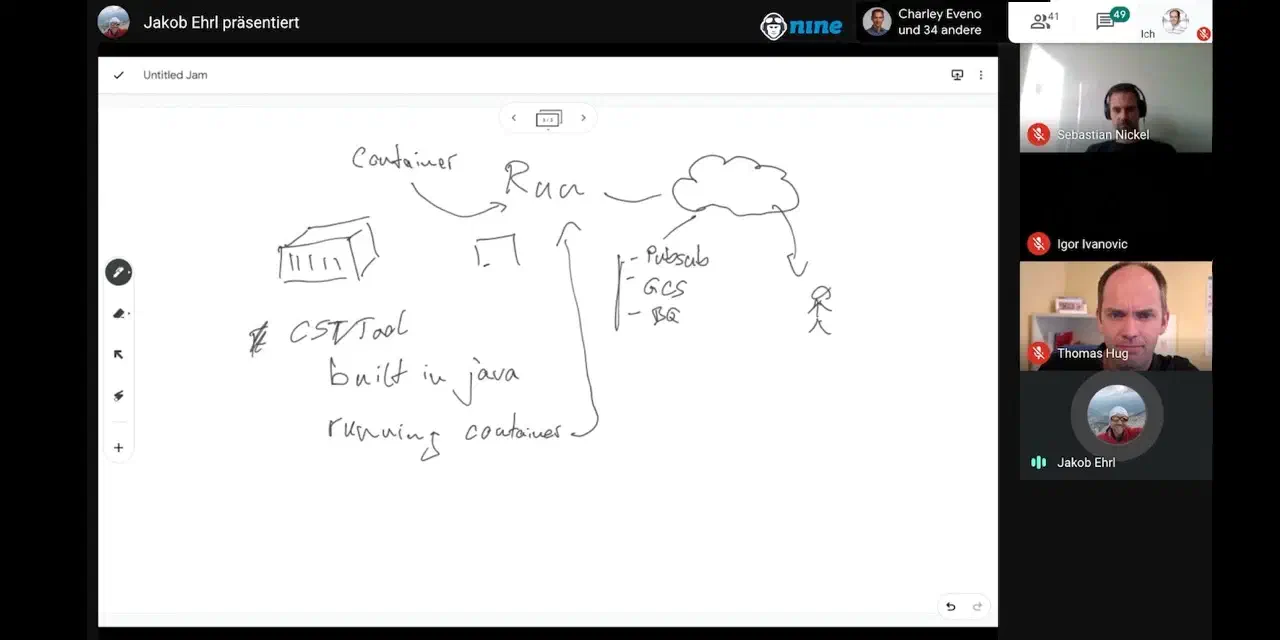
The Google Cloud Meetup #4 took place on 19 May 2020 for the first time on Google Meet. In …
Processing authoritative requests As every now and then we receive requests by authorities to …

bespinian runs its AI stack Keera on Deploio, our Swiss PaaS, keeping the product's sovereignty …
Demokratis is bringing Swiss democracy into the digital age – for cantons and public authorities …
In late 2024, swissICT faced an unexpected crisis: the previous operator of the ICT Salary Survey …

For the relaunch of supertext.com, Supertext needed a new GPU cluster that required more power …
We supported Peak Privacy in designing and building a specialized server infrastructure for LLM …

We helped Renuo AG to smoothly transition everything that was running on Heroku to Deploio, our own …

We helped mühlemann+popp to smoothly realise the migration from the Google Cloud to the Nine …

We supported healthinal with the implementation of a new monitoring system based on Managed …

We have been instrumental in helping cab to implement an outstanding hosting solution that offers …

We helped Stadler Form to find the right technical solution. At the same time, there were some …

Nine operates the reliable and stable infrastructure for PUPIL, an all-in-one solution for digital …

Nine operates the highly available infrastructure for the Ayyah software based on the Nine …
Nine was involved in the project with consulting and implementation services and support. According …

Through workshops, consulting, and their Kubernetes service stack, built atop GKE, Nine helped …

Clientis needed a solution to satisfy the requirements of the Swiss Financial Market Supervisory …

Through comparis.ch, users can compare everything from health insurance schemes and insurance …

With our Root Servers, the Swiss Red Cross achieves complete independence on an efficient …
When outsourcing the hosting of www.mobiliar.ch and other web projects as part of its brand …

New market conditions, new requirements for their product range: containerizing their software has …
With the Managed Virtual Servers, HUG AG benefits from an all-round carefree package including …

Nine provided the expertise, training and optimisation. Through workshops, consulting, and their …

Nine provided the expertise through workshops, consulting, and the services built atop GKE. All …

The Dr. Marc Rutschmann AG is using Managed Kubernetes for creating and managing customer web pages.
Airlock Microgateway protects your applications on Managed Kubernetes against web attacks, directly through the Kubernetes Gateway API and without a sidecar. We install and operate the operator for you, you attach your apps using standard Gateway API resources. Airlock is available already from CHF 427.– per month (up to 1 million requests/month), with further tiers up to 10 million requests. You can find all tiers in the Price Calculator and for more technical details, please check our Documentation.
Airlock Microgateway is a Kubernetes-native web application firewall (WAF) from Swiss manufacturer Ergon, which we operate for you on Managed Kubernetes (NKE). Sidecarless via the Kubernetes Gateway API, with identity-aware proxy functionality and entirely on Swiss infrastructure.

We operate, monitor and patch the Gateway infrastructure. You still configure and maintain your own WAF rules through the Airlock resources in your own namespace, tailored to your application.

Runs sidecarless via the Kubernetes Gateway API, directly inside your Managed Kubernetes cluster, instead of as an upstream external service.

The WAF inspection takes place in your cluster in our Swiss data centres, not in an external service in front of it. This matters for industries with data location requirements.

OIDC- and JWT-based access control right at the Gateway, without running an additional reverse proxy component.
We operate the Airlock Microgateway operator and the Gateway infrastructure, you attach your applications using standard Gateway API resources and define your own security policies.
Features in detail
Setup & operations: We install the Airlock Microgateway operator on your Managed Kubernetes cluster and create one or more Gateways in the Nine-managed nine-system namespace, each with its own load balancer IP and stable hostname.
Certificates: Let’s Encrypt ClusterIssuers for your domains, issued and renewed automatically.
Attachment: You create ListenerSet and HTTPRoute resources in your own namespace to attach your application to the Gateway and route traffic.
Operations & maintenance: Monitoring, patching and license management of the operator are on us, not on you. You don’t need to build or maintain in-house WAF expertise on your team.
Protection against the OWASP Top 10, including DoS limits, header filtering and CSRF protection, plus JSON parsing for structured attack detection.

Validation of OpenAPI specifications and GraphQL schemas, so only requests that match your API definition get through.
Configured exclusively through the Kubernetes Gateway API, no sidecar container needed in your application pods.
OIDC relying party support, token introspection and JWKS-based JWT validation with claims- and path-based access control right at the Gateway.

Identity information is passed through to your backend, for single sign-on without an extra component of your own.

Define your own error pages and responses, every request logged in structured form and, with Loki enabled, visible directly in Grafana.
Staging and test environments have their own tiers, from CHF 42.70 per month (up to 1 million requests, cumulated across all non-production gateways). You can find all tiers in the Price Calculator. For more than 10 million requests per month, contact us.
We are certified to ISO 9001 and ISO/IEC 27001 for quality management and information security, this also covers the infrastructure your Managed Kubernetes cluster runs on.
No US or other third-country provider sits between the Gateway and your backend.

Airlock Microgateway is a Swiss security solution from Ergon, which we operate on our own Swiss infrastructure.
Your Managed Kubernetes cluster runs on our own hardware in Swiss data centres, without rented hyperscaler compute in the background.
Airlock Microgateway is not currently self-service, setup happens together with us.
1. Get in touch – tell us about your expected request volume and requirements.
2. Setup by us – we install the operator and create one or more Gateways on your Managed Kubernetes cluster, including automatic TLS certificates.
3. Attachment by you – you create ListenerSet and HTTPRoute resources in your own namespace and define your security policies.
4. Operations – we take care of monitoring, patching and license management for the operator.
We'll discuss, without obligation, whether and how Airlock Microgateway fits your Managed Kubernetes cluster.
Nine supported us perfectly with their Managed Kubernetes solution to migrate our customer's application from Google Cloud to a purely Swiss infrastructure.

We can highly recommend Nine as an uncomplicated, highly professional provider.

Thanks to the collaboration with Nine, we can concentrate on what we do best: Developing software solutions for the healthcare sector. The infrastructure runs securely and reliably in the background so that we can offer our customers the best solutions. With Nine, we have a strong, local and reliable partner at our side.

bespinian runs its AI stack Keera on Deploio, our Swiss PaaS, keeping the product's sovereignty promise without operating a platform of its own.
Read more: KeeraDemokratis is bringing Swiss democracy into the digital age – for cantons and public authorities that won't compromise on data protection or server …
Read more: DemokratisIn late 2024, swissICT faced an unexpected crisis: the previous operator of the ICT Salary Survey shut down their business. What began as a crisis …
Read more: swissICT Salary Survey
We moved our managed services and Deploio from ingress-nginx to HAProxy. Eight defaults behaved differently. Here is …
At TechTalk #29, Thomas Jaggi (LegacyNotes) showed live how much modern browsers and Node.js now handle natively, no …
In August 2026, a large DDoS attack hit a customer and our own network directly. What happened, where our defences fell …
At TechTalk #29, Lena Fuhrimann (bespinian) shared a practical guide to running fast, private LLMs yourself, from …
At TechTalk #29, Sebastian Nickel walked us through our journey from Ingress-NGINX to HAProxy and Gateway API, and the …
An overview of how to manage your infrastructure at Nine through code: the Nine API, nctl, Deploio, Terraform, Ansible …
Do you have questions about our products? No problem. Contact our sales department or go directly to your Cockpit to see all the possibilities at Nine.
